Secrets: Shared providers
Catalog id: resource.secrets.sharedProviders
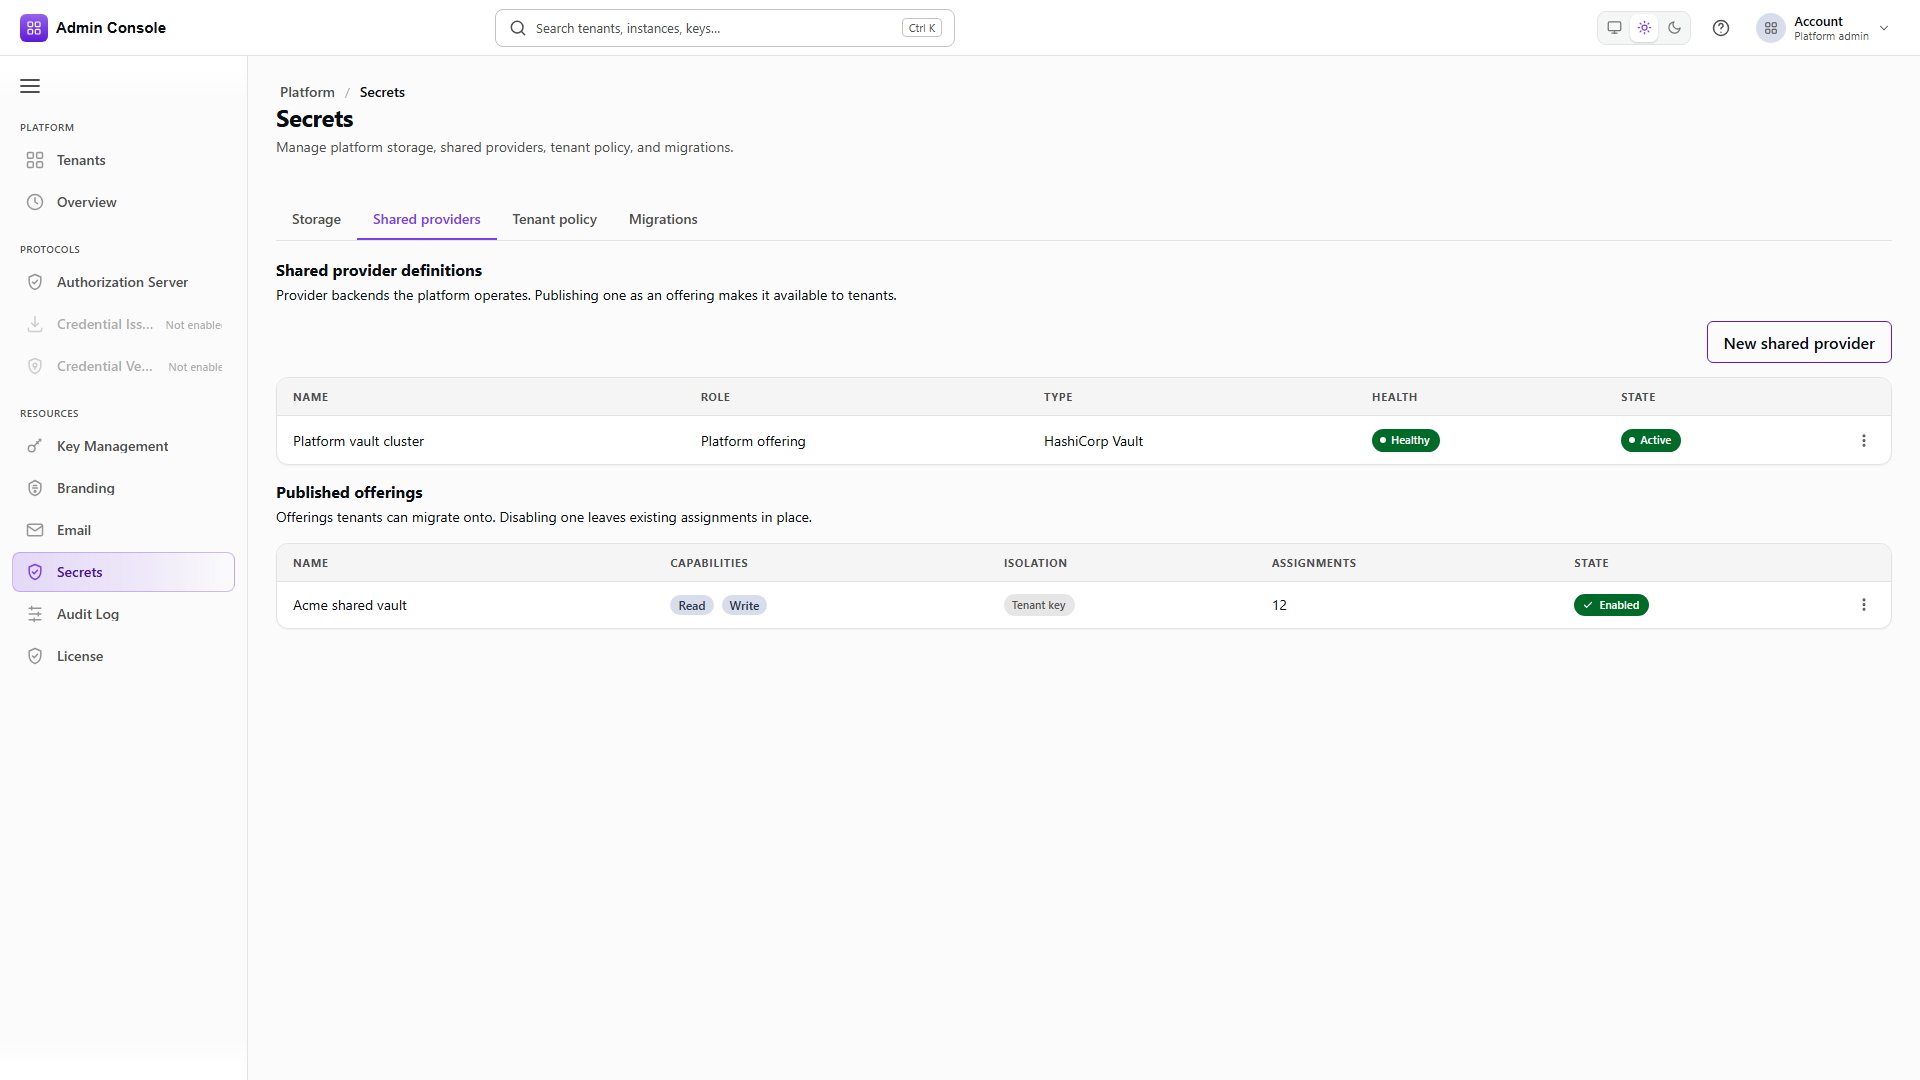
A shared provider is a secret backend the platform runs and then offers to tenants, so a tenant can hold secrets without operating a vault of its own. Publishing one as an offering is what makes it selectable; until then it exists but no tenant can adopt it.
This page is platform-scoped. What a given tenant is allowed to adopt is decided on Tenant policy, not here.
Audience: platform operator.
Guide: Secrets and KMS providers.
What an offering says
Tenants adopt an offering by its offeringId, and that id is written into their configuration.
Renaming one is therefore not a cosmetic change. displayName is what an operator reads when
choosing, and it is the only human-readable handle they get, so two backends that differ only in
purpose need names that say which is which.
isolationMode describes how tenants are kept apart inside a backend they share. With
tenant-key, each tenant gets its own key inside one backend, which is what makes offering a shared
vault reasonable in the first place.
assignmentCount tells you how many tenants currently use the offering, and it is the number to
look at before you touch anything. Rotating the credential or disabling an offering that twelve
tenants depend on reaches all twelve. enabled controls whether tenants may adopt it from now on;
turning it off stops new adoption and leaves the existing assignments in place, so it is a way to
retire an offering gradually rather than a way to cut tenants off.
List the published offerings
- Admin Console
- Request
- Response
- Try it
Open Resources > Secrets > Shared providers in the platform scope. Check assignmentCount
before changing anything about an offering: the number tells you how many tenants a credential
rotation or a disable will reach.
Full schema: Secret Management API.